## Related terms

- workspace
- user
- settings
- campaign

See the [glossary](/glossary.md) for definitions.

---

# Synerise MCP Server


<div class="admonition admonition-important"><div class="admonition-icon"><svg xmlns="http://www.w3.org/2000/svg" fill="none" viewBox="0 0 24 24" stroke="currentColor" stroke-width="2.5"><path stroke-linecap="round" stroke-linejoin="round" d="M12 8v4m0 4h.01M21 12a9 9 0 11-18 0 9 9 0 0118 0z" /></svg></div><div class="admonition-body"><div class="admonition-content">

This feature is available in [public preview](/docs/log-in-and-navigate-synerise-platform#public-preview) mode.

</div></div></div>


In the **Synerise MCP Server** settings, you decide whether AI clients outside Synerise, such as Claude or Cursor, can connect to your workspace through the [Synerise MCP Server](/developers/mcp/overview), and which actions they can perform there.


<div class="admonition admonition-warning"><div class="admonition-icon"><svg xmlns="http://www.w3.org/2000/svg" fill="none" viewBox="0 0 24 24" stroke="currentColor" stroke-width="2.5"><path stroke-linecap="round" stroke-linejoin="round" d="M12 9v2m0 4h.01m-6.938 4h13.856c1.54 0 2.502-1.667 1.732-2.5L13.732 4c-.77-.833-1.964-.833-2.732 0L4.082 16.5c-.77.833.192 2.5 1.732 2.5z" /></svg></div><div class="admonition-body"><div class="admonition-content">

External AI clients may receive personal data or other sensitive information from your workspace. See [Data privacy and third-party AI clients](/developers/mcp/overview#data-privacy-and-third-party-ai-clients) before you enable access. For answers to questions about the EU AI Act and data processing, see the [Synerise MCP Server FAQ](/developers/mcp/faq).

</div></div></div>


## Prerequisites
---

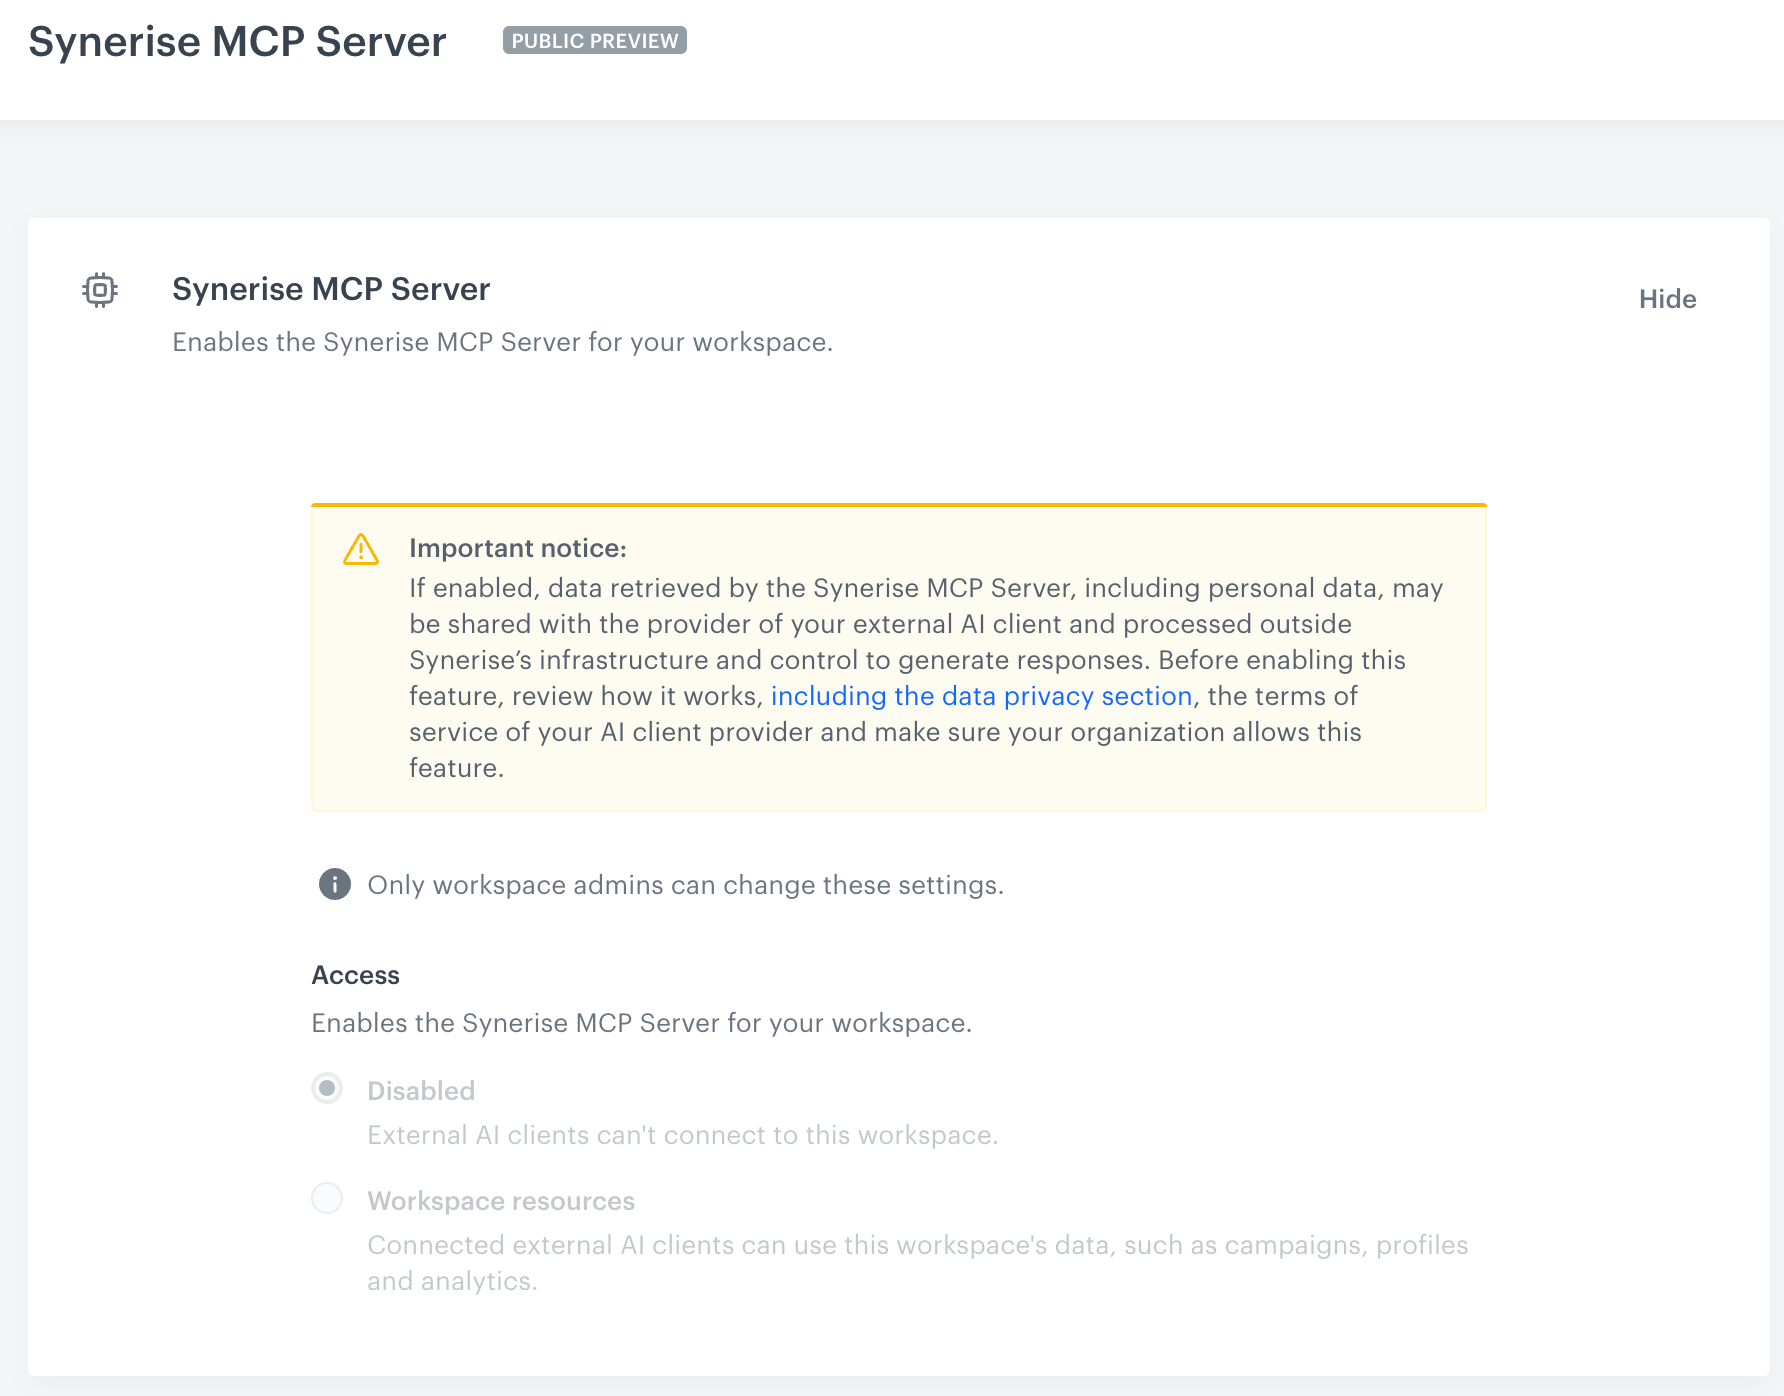
Only users with the PROFILE_ADMIN role can change these settings. Users with other roles can only view them.

## Access levels
---

| Option | What external AI clients can do |
|---|---|
| **Disabled** (default) | External AI clients have no access to the workspace. |
| **Workspace resources** | External AI clients can access the resources in your workspace, such as campaigns, analyses, and profiles. |

## Allowed actions
---

When you select **Workspace resources**, you also decide which actions external AI clients can perform on the resources:

- **Read** - clients can browse and view resources. This action is always enabled.
- **Write** - clients can also create and edit resources. This action is optional.

The **Delete** and **Execute** actions can't be selected.

### Allowed actions and user permissions

An external AI client acts on behalf of the user who connected it, so it can only perform actions that are both allowed in the workspace settings and permitted by that user's [permissions](/docs/settings/identity-access-management/permissions). For example, if a user has no access to campaigns, the client can't access campaigns for that user, even if **Read** is allowed in the workspace.

When **Workspace resources** is selected, the **AI Agents** > **MCP Server** permission appears in the role permission matrix. By default, this permission is granted to the [basic roles](/docs/settings/identity-access-management/permissions#basic-roles) (PROFILE_ADMIN and PROFILE_MANAGER) and to the [predefined Synerise roles](/docs/settings/identity-access-management/permissions#predefined-synerise-roles), so users with these roles can connect external AI clients without any changes to their roles. For custom roles, you must grant the permission yourself in the [role permission matrix](/docs/settings/identity-access-management/permissions#permissions). You can also use the permission to limit the actions of external AI clients for specific roles. For details, see ["AI Hub permissions"](/docs/settings/identity-access-management/permissions/ai-hub-permissions#use-the-synerise-mcp-server). Changes to the **MCP Server** permission in a role can take up to 5 minutes to take effect.


<div class="admonition admonition-note"><div class="admonition-icon"><svg xmlns="http://www.w3.org/2000/svg" fill="none" viewBox="0 0 24 24" stroke="currentColor" stroke-width="2.5"><path stroke-linecap="round" stroke-linejoin="round" d="M13 16h-1v-4h-1m1-4h.01M21 12a9 9 0 11-18 0 9 9 0 0118 0z" /></svg></div><div class="admonition-body"><div class="admonition-content">

The permissions of predefined Synerise roles are fixed, so you can't remove the **MCP Server** permission from these roles.

</div></div></div>


## Configuring access
---

1. Go to <img src="/api/docs/image/12052597dc27ec063ccaf318d610624067207409/icons/settings-icon.svg" alt="Settings icon" class="icon"> **Settings > Synerise MCP Server**.
2. Click **Show**.
3. In the **Access** section, select **Disabled** or **Workspace resources**. For details about the options, see [Access levels](#access-levels).
4. Optionally, if you selected **Workspace resources**, in the **Allowed actions** section, select **Write** to let external AI clients create and edit resources.
5. Click **Apply**.  
    **Result**: The settings summary shows the selected access level and allowed actions.

<figure><img src="/api/docs/image/12052597dc27ec063ccaf318d610624067207409/docs/settings/_gfx/mcp-server-settings.png" class="large" alt="Synerise MCP Server settings with an important notice about sharing data with the provider of an external AI client, and the Access section with the Disabled and Workspace resources options, unavailable for a user who isn't a workspace admin"><figcaption>Synerise MCP Server settings as seen by a user without the PROFILE_ADMIN role</figcaption></figure>

After you enable access, users can connect their AI clients as described in [Getting started](/developers/mcp/getting-started).

## Related articles
---

- [Overview](/developers/mcp/overview)
- [Synerise MCP Server FAQ](/developers/mcp/faq)
- [System Agent](/docs/settings/agentic-ai/system-agent)
