The Decrypt Data transformation step lets you decrypt values in selected columns of a dataset. Paired with the Encrypt Data step or an external encryption tool, it enhances data security and confidentiality by encrypting sensitive information with AES-256 key using AES-GCM mode that is unreadable without a decryption key.
By using this transformation, you can safeguard your data and comply with privacy regulations while maintaining the integrity of your dataset.
Requirements
- You must have a user role with the following permission: Settings > Encryption keys > Read. This permission lets you see the list of encryption keys in the Encrypt Data and Decrypt Data steps.
- Create an encryption key in Synerise
- You must encrypt the column values (not the column header) using the AES-GCM encryption algorithm with a 256-bit secret key, in the following format:
base64encode([IV] + [Encrypted Text] + [Authentication Tag]), whereIVis the initialization vector used to initiate the encryption algorithm.
Step configuration
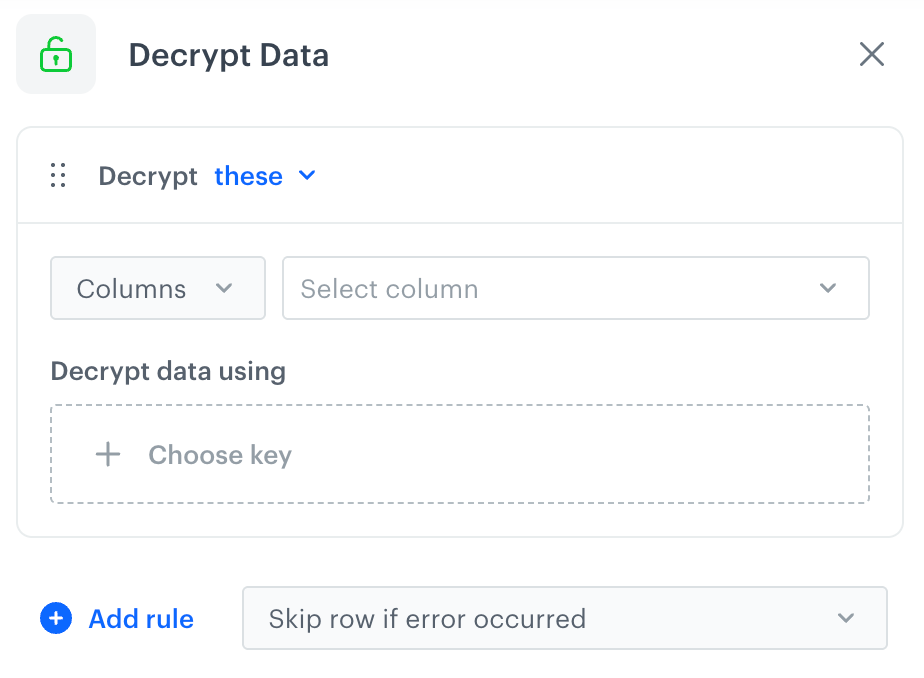
- In the Data Transformation Studio, add the Decrypt Data step.
- Indicate the columns whose values will be decrypted.
- In the Decrypt data using section, click Choose key and select the key with which the data will be decrypted.
- To add more rules, click Add rule and repeat steps 2-3.
- To define what happens if rows contain errors, from the dropdown list next to Add rule, select one of the error handling options.
- Confirm the settings by clicking Apply.
- You can check the result in the Output tab.
Selecting columns
In each rule of the step, you indicate the columns on which the operation is performed.
- In the header of the rule, click these and select one of the options:
- these - the operation is performed on the columns you indicate.
- all except these - the operation is performed on all columns except the ones you indicate.
- From the first dropdown list in the rule, select how you want to indicate the columns:
- Columns - from the Select column dropdown list, select one or more columns.
- Where name - define a condition (a dynamic condition) that the column names must meet. Select a logical operator (Ends with, Starts with, Contain, Not contain, or Regex) and enter the value. For example, if you select Starts with and enter
pro, the operation is performed on the columns whose names start withpro
Column names are case-sensitive, for example,productdoesn't matchProductCode. A regular expression must match the entire column name, for example,product.*matchesproductName, butproductdoesn't. To ignore the letter case in a regular expression, add(?i)at the beginning, for example,(?i)product.*
You can't combine dynamic conditions with the all except these option.
Dynamic conditions are especially helpful when you use a JSON file as sample data. When a JSON file contains an object deeper than the root object, its items are transferred to the transformation as separate columns named {object}.{parameter}. You can't add those columns from the Select column list, but you can include them with a dynamic condition, for example, by including columns whose names contain the name of the object they were created from.
Handle errors
You can define what happens with rows in which the step fails (for example, as a result of Jinja rendering). From the dropdown list next to Add rule, select one of the following options:
- Skip row if error occurred - It omits the row when an exception occurs.
- Skip if result is null or empty string - It omits rows with empty strings and
null(which may be the result of rendering Jinja). - Stop further transformation - The transformation stops at the row with an error. The data before the line that caused the error is transformed (and imported if the transformation is used in the Data Transformation Studio node).
- Insert null if error occurred - Wrong values are replaced with
null. If you use such a transformation for the import of profiles, the existing value of an attribute is cleared and replaced with thenullvalue. - Insert empty string if error occurred - Wrong value is removed and the cell remains empty.
Example of use
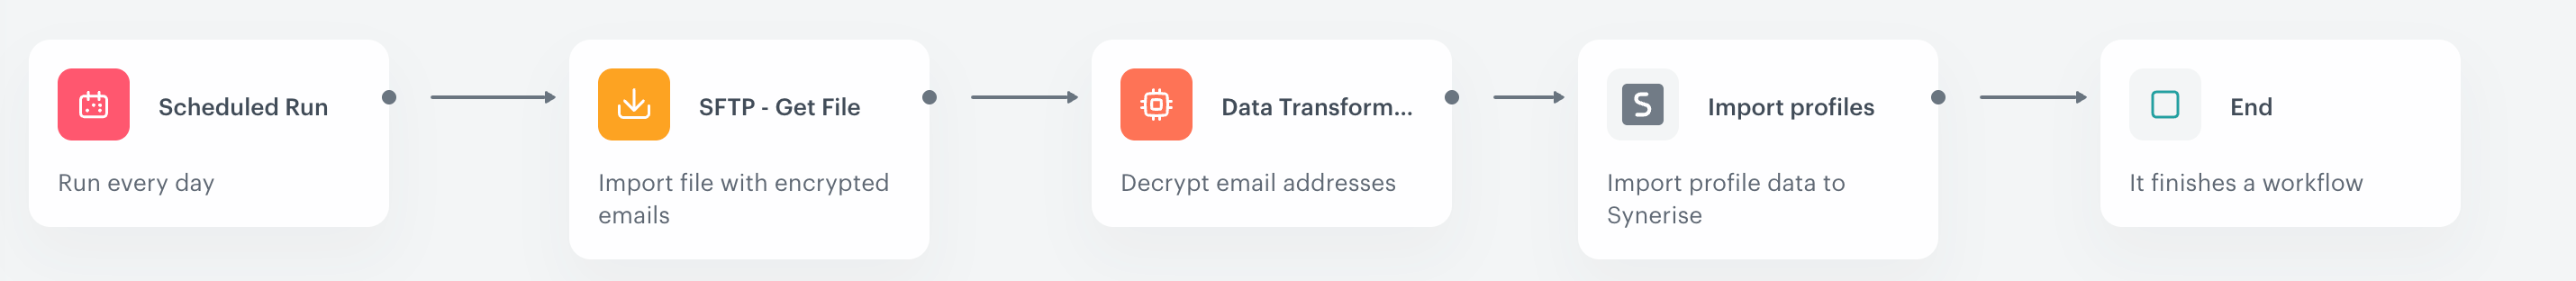
You can use the Decrypt Data step to decrypt a set of sensitive data you receive in Synerise. For example, you want to decrypt a column in a CSV file that contains email addresses of your customers. This example of use contains instructions how to create a transformation that decrypts a set of sensitive data. You can use the transformation in the "Data Transformation Studio" node in a workflow that retrieves the file from an external source, decrypts email addresses, and imports them to Synerise.
Before you proceed to creating a transformation that uses this step, ensure that you meet the requirements.
Sample data used in this example
email,newsletter agreement HbXwKJulDVa9VblCWhraOHSKo61w5kZfMFwKkEF5zJOQ5DJar108bYyf8Jd7HZJT,yes oIMNS9VUuwhirdXftfUPOKKmlzaAV21GofOqAb/yEYudwYzjYlOKdwmUf9aOl3CMHjc=,no b1etJupv9xyhHhMlGoaHi1gAqEEioy/3igxYdXXLPJe1gZCUvc7aR0PUe6LS6t6+Yxfr,yes y6THLdsxjxCLUTv1spFN4iwFTVhaaOL6c4fSadQ0+fgMDkiB86lP1Zpx+20QfNHSKQQ=,yes sGV7bJiCL448OfAf/ZUPn8tKzsOyWIg06ukFcyGogOidx6pLt/s4sQ0VusAfV+HulEkjMIw=,no- In the Data Transformation Studio, add sample data which imitates the structure of the data that will be transformed in the workflow.
- Click Add step and select Decrypt Data.
- From the Select column dropdown list, select the email column.
- In the Decrypt data using section, click Choose key and select the Synerise encryption key which will be used to decrypt data in this column.
- Confirm the settings by clicking Apply.
Result: In the Output tab, the values in the email column are decrypted.
In the further steps, you can create a workflow that is triggered repeatedly, retrieves a file with encrypted email addresses, decrypts email addresses by means of the transformation created as described above, and imports customers with these decrypted email addresses to Synerise.